
When a company starts growing, many good things happen at once. New teammates join. More customers sign up. Someone suggests a new app that will “make everything easier.” Another team wants to try a different cloud platform. In just a year, the company looks very different.
All that growth is exciting, but it quietly changes your risk. Every new tool, device, and connection adds to your digital attack surface. In simple words, that is the total set of doors, windows, and side entrances that an attacker could try.
When the business is small, you can almost list those things from memory. As you grow, that gets harder, and then it becomes almost impossible without some structure.
How Growth Creates Hidden Risk?
Think about what happens in a normal year for a growing company. You hire people. Each one gets a laptop, some accounts, and access to internal systems. Your product team spins up new test environments.
A contractor needs a quick login. The marketing team tries three different email tools before settling on one. Sales signs up for a new CRM without looping in IT, because “we need it this quarter.”
None of this feels like a security event at the time. It is just work. But each action leaves a trace behind. Test servers that nobody remembers.
Old accounts that were never removed. Extra admin rights that felt easier at the time. Multiply that by a few years of growth and you end up with a lot of stuff you cannot fully see.
Attackers know the score. They are not always trying to break your strongest lock. They are often looking for the unlocked side door that somebody forgot to close. That might be an old demo site, a small integration, or a personal device that has more access than it should.
Getting A Real Picture Of Your Assets
So where do you start? Most growing companies reach a point where someone asks a very basic question, “Can we get a proper list of what we have out there?” It sounds simple. In practice, it can be messy.
You need more than a list of servers or one cloud account. You want to know about domains, subdomains, web apps, APIs, databases, user devices, and even tools that live in different departments. You also want to see which third party services plug into your systems or handle your data.
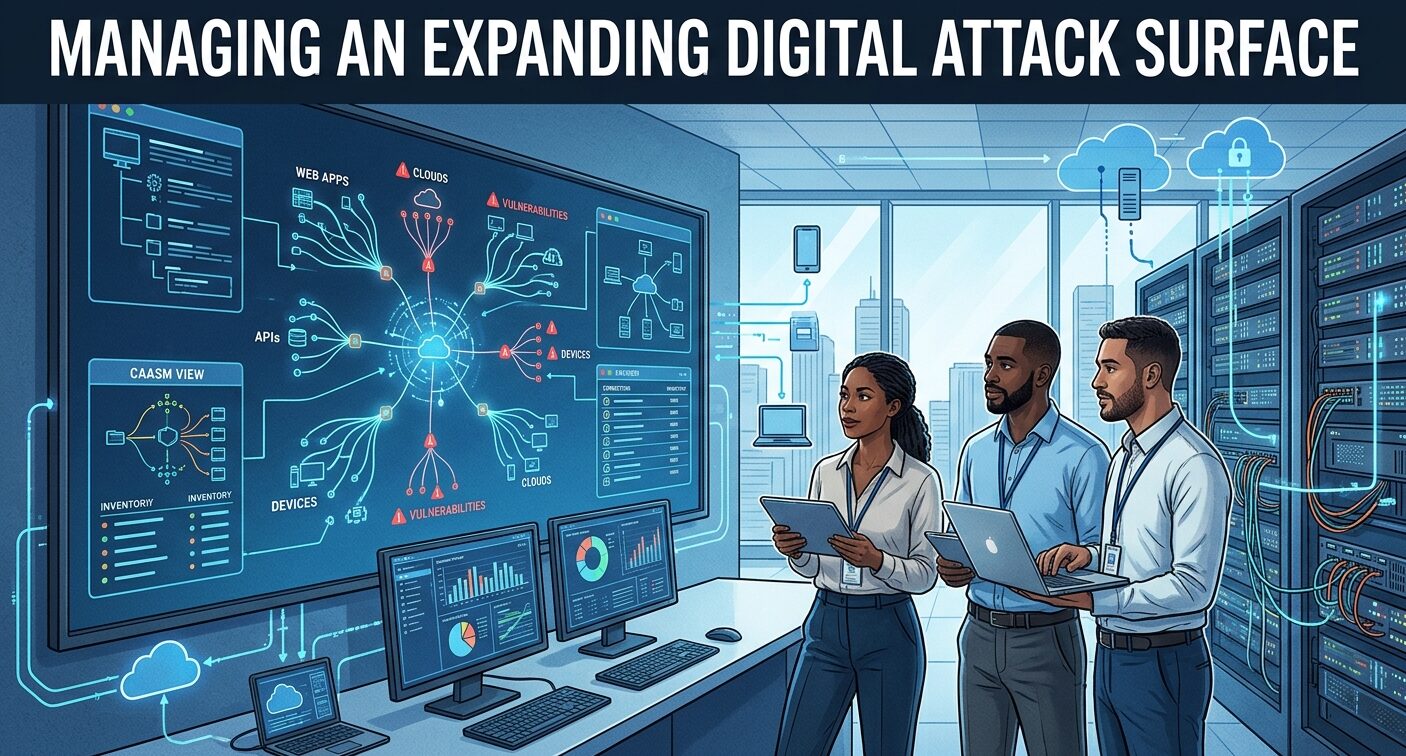
This is where more structured approaches start to help. Many teams are now looking at Cyber Asset Attack Surface Management (CAASM) to deal with this problem. The idea is not a magic tool, but a way of pulling data from many places into a single, up to date view.
Instead of ten half finished spreadsheets, you get one living map of your assets, where they sit, and how they connect. For a company that is changing every month, that kind of live view is much more useful than a one-time audit.
Deciding What To Fix First
Once you see your attack surface more clearly, the next question appears. What do we do first. You cannot resolve every single issue at once, and that is fine. The real skill is choosing what matters most.
A simple way to start is to look at impact. Which systems hold customer data. Which ones handle money. Which ones are needed for day to day work. Which ones are exposed to the public internet. If a system sits in all of those groups, it is a clear priority.
You can even rate systems in plain language. For example, “If this goes down, can we still operate.” or “If this is hacked, do we have to tell customers.”
When you line up your assets against questions like that, a clear priority emerges. You might see that a small internal tool can wait, while an old public login page needs attention this week.
Nailing The Basics As You Grow
A lot of security problems come from basic things that stayed broken for too long. Old software that was never updated.
Services that were left open to the internet. Shared passwords inside a team. Extra admin rights given “just for now” that nobody ever removed.
For growing companies, getting the basics right is not boring, it is powerful. Strong, unique passwords, multi factor authentication, regular patching of important systems, and turning off what you do not use will stop a huge number of common attacks. It is not fancy, but it works.
This is also where small bits of automation help. You can set simple rules such as “no new user without multi factor authentication” or “no new cloud server without these minimum settings.” Once these rules are in place, every new step the company takes is slightly safer by default.
Bringing People Into The Picture
Tools and platforms can only do so much on their own. The people in your company see a lot that tools miss.
A developer might notice that someone pasted a password into a chat. A support agent might feel uneasy about how a shared inbox is handled. A sales rep might sign up for a trial service and then realise it asks for far too much access.
The important question is, do they feel safe to say something? In many fast-moving teams, people worry that raising a concern will slow things down or lead to blame. So they stay quiet, and small issues grow into bigger ones.
Leaders can change this dynamic with small habits. Thank people who raise possible risks, even if they turn out to be nothing.
Explain clearly who to talk to when they see something odd. Keep security conversations short and regular, not long and rare. Over time, such behaviour builds a mood where security is everyone’s job, not just the IT team’s problem.
Preparing For The Bad Day
Even with good habits, incidents can still happen. A laptop can be stolen. An account can be phished. A vendor you rely on can be attacked. Pretending such an event will never happen does not help. Planning for it does.
You do not need a huge, complex plan. Start with a few clear points. Who gets called first? Who has the right to shut something down? How do you decide if customers need to be told? Where do you write down what happened, so you can learn from it later.
When people know the answers in advance, they are less likely to freeze or panic. The company can act faster and speak more clearly, which can reduce damage and protect trust.
Conclusion
Managing an expanding digital attack surface is part of growing up as a company. At first, it feels like a side job. Over time, you realize it is closely tied to your ability to keep serving customers and protect their trust.
The companies that handle this process well do a few simple things. They work to understand what they actually have.
They focus on the systems that matter most. They keep the basics strong with every new step they take. They listen when people speak up. And they accept that mistakes will happen, so they prepare to deal with them calmly.
When you treat security as part of how you grow, not a task you add at the end, your attack surface becomes something you can manage instead of fear. That makes growth feel a lot more solid, for you and for the people who trust you with their data.
